COOKIE NOTICECOOKIE CHOICE

We use cookies for analytics (Google Analytics) and ad measurement (Google Ads, including remarketing, and ChatGPT Ads by OpenAI). Strictly necessary cookies keep the site working. See our Cookie Policy for what each one does and how to opt out.

We’d like to use cookies for analytics (Google Analytics) and ad measurement (Google Ads, including remarketing, and ChatGPT Ads by OpenAI), and none of them is set unless you accept. Cookie Policy

About TCSA

The team behind
1,000+ audits since 2017.

Tranquility Cybersecurity (TCSA) is a security and compliance consultancy with offices in Gurugram and Bengaluru. Our work is led by Surendra Pal Singh, who has spent twenty-five years in information security and serves as our Chief Information Security Officer and Data Protection Officer.

We prepare companies for SOC 1, SOC 2, ISO 27001, DPDP, HIPAA, GDPR, ISO 42001 and more than a dozen other frameworks, and our own team runs the penetration tests.

One square, one audit
  • SOC 2
  • SOC 1
  • ISO 27001, DPDP, HIPAA and the rest
A thousand squares for the 1,000+ audits we have prepared teams for since 2017. More than 300 were SOC 2 and more than 100 were SOC 1.
  • 21K School
  • Arali AI
  • Assemblage Health
  • Cargoflash
  • Data Alchemy
  • Dsider
  • Factor Avenue
  • GroundHog Apps
  • immiOne
  • IPPC Group
  • LiveMindz
  • Lyik
  • NPCI
  • Phyllo
  • Softsages
  • Surface Labs
  • Vault Infosec
  • Xonar
  • Harriman Global
  • Dune Dynamics
  • Aairo
  • Ardem
  • autoResilience
  • Citius Cloud
  • Datavi Cloud
  • eSolutions
  • Forsys
  • HighRadius
  • Intellify
  • Jarex
  • LookDeep Health
  • Mashreq
  • PayU
  • Provar
  • Soudah Development
  • TalentBridge
  • VisiLean
  • Zepic
  • Procedure
  • incep²t
  • American Express
  • Ascent Risk & Resilience
  • Auxanova
  • Cohivra
  • DollarTraq
  • Excers Technologies
  • Girmiti
  • IIIT Delhi
  • intelXIP
  • Komp AI
  • Loveinstore
  • Maxima
  • Personaify
  • Sebone Technologies
  • Spinny
  • Uni5
  • WyraAI
  • JudoNxt
  • BuyNxt · Green Receipt
Our story

Since 2017, one team at a time.

2017

Where it began

TCSA started in 2017 to give growing companies the security and privacy leadership that large enterprises keep in-house. Surendra Pal Singh brought his experience of running security programmes to that work, and he leads it today as our CISO and DPO.

Startups

Small teams, large customers

Much of our work has been with startups in Bengaluru, Gurugram, San Francisco, Delaware, Singapore and Malaysia. Many had a large customer asking for a SOC 2 report or an ISO 27001 certificate and no security team of their own. We wrote their policies, set up the controls with their engineers and sat beside them when the auditor asked questions.

Breadth

More frameworks, our own testers

As those companies grew, so did the range of the work. We now prepare teams for more than 20 frameworks, from SOC 1 and ISO 27001 to DPDP, GDPR, HIPAA and ISO 42001 for companies building with AI. Our own penetration testers have found more than 10,000 vulnerabilities along the way.

Teaching

Passing it on

We also teach what we practise. More than 500 professionals have been through our training, including our ISO 27001 Lead Auditor course.

2026

Today

In 2026 the practice became Tranquility Cybersecurity Services Private Limited, with offices in Gurugram and Bengaluru and clients in India, the US, the UK, Australia and the UAE. We have prepared teams for more than 1,000 audits, more than 300 of them SOC 2.

The people

The controls and the books, at one table.

Our security team builds and runs the controls an auditor tests. IPPC Group, the chartered accountancy firm founded in 1978 and a member of Russell Bedford International, has spent nearly five decades in audit and tax. We work side by side, so the questions your buyer’s security team asks and the questions their finance team asks are answered by people who already sit together.

Leadership

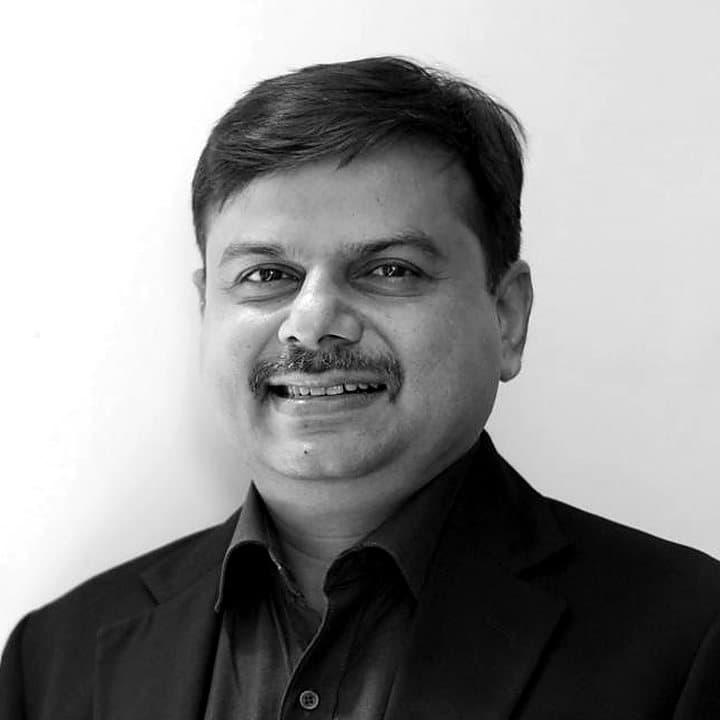
  • Surendra Pal Singh

    Surendra Pal Singh

    Chief Information Security Officer and Data Protection Officer

    Twenty-five years in information security. Surendra holds the two roles our clients most often need to fill, so the advice a founder gets on an access review, a vendor questionnaire or a breach notice comes from someone who answers for the same things himself.

    CISA · ISO 27001, 27701 and 42001 Lead Auditor · MCSE · ITIL

  • Parth Chauhan

    Chief Compliance Officer and Co-Founder

    An electronics engineer from BITS Pilani who wrote firmware at Micron before he moved into audit. Parth leads our SOC 2, ISO and privacy delivery and our testing practice, and stays with each engagement until the signed report is in the client’s hands.

    ISO 27001, 27701 and 42001 Lead Auditor · CEH

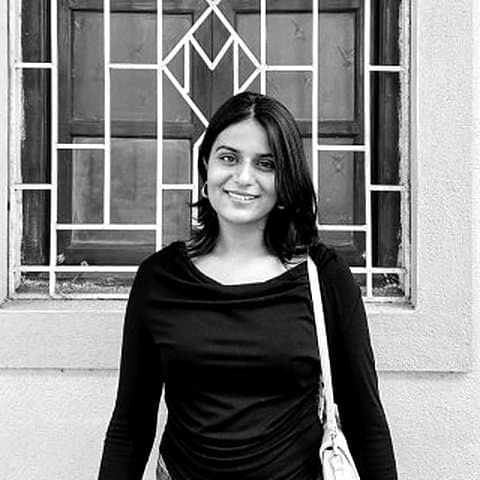
  • Saundhi Chauhan

    Saundhi Chauhan

    Lead Auditor

    Saundhi runs our engagements from the first call, through scoping, the kickoff and the questionnaires that show where a client really stands. She leads ISO 27001 and ISO 27701 work as a certified lead auditor for both standards.

    ISO 27001, 27701 and 42001 Lead Auditor

Partner

  • Rajendra Bohra

    Partner

    Rajendra works on site at the companies where we serve as virtual CISO, running internal audits, change reviews and the policies engineers follow day to day. Before TCSA he spent nine years leading information security and IT for a global customer-experience company across five data centres.

Advisory Board

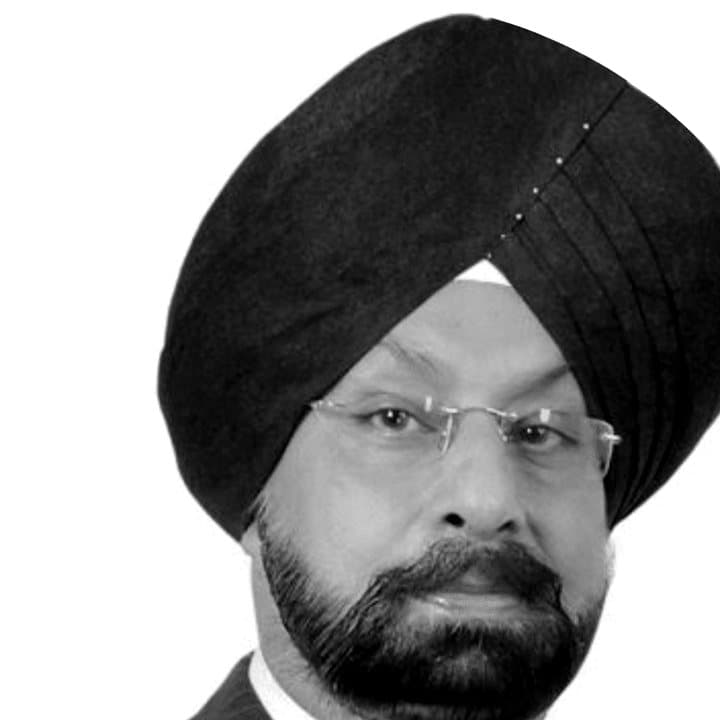
  • CA Inderpal Singh Pasricha

    CA Inderpal Singh Pasricha

    Founder and Senior Partner, IPPC Group

    Inderpal founded I.P. Pasricha & Co in 1978 and built it into IPPC Group, a member of Russell Bedford International. He brings five decades of audit, tax and corporate practice to the questions our clients’ finance teams ask.

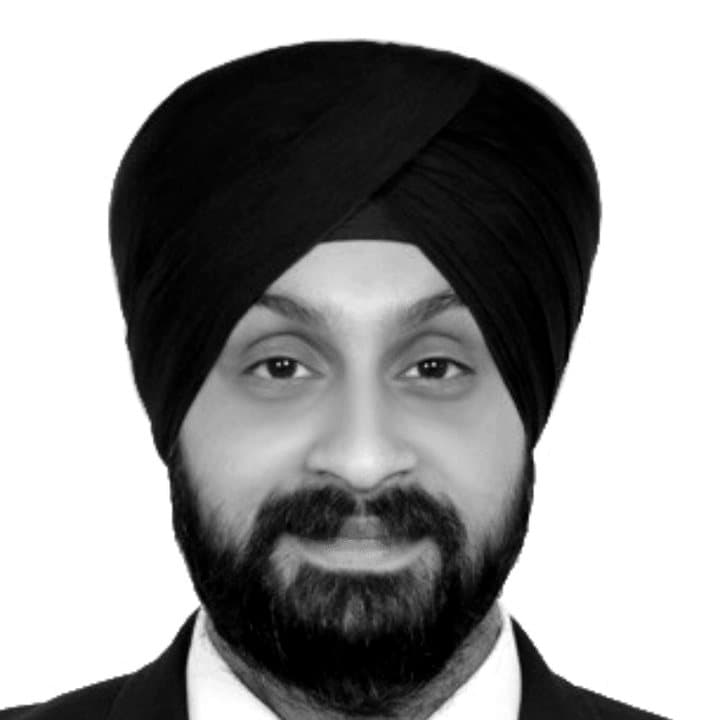
  • CA Maneet Pal Singh Pasricha

    CA Maneet Pal Singh Pasricha

    Managing Partner, IPPC Group

    Maneet leads IPPC’s tax practice, across corporate tax, transfer pricing and mergers, after KPMG and Deloitte. He advises us on the finance and tax side of the companies we work with.

The wider team

Around them work our consultants, lead auditors and penetration testers in Gurugram and Bengaluru. Between them they hold CISA, CISSP, CEH and OSCP certifications and lead auditor qualifications for ISO 27001, ISO 27701 and ISO 42001.

Client stories

Three teams and how they got there.

A GTM platform, an AI platform for commercial real estate and a quote-to-cash consultancy. Different products and different deadlines, each ending in a signed report.

Wyra

GTM AI platform

2 monthsfrom kickoff to the SOC 2 Type 1 report and ISO 27001 certification

How Wyra reached SOC 2 Type 1 and ISO 27001 within two months

Wyra builds a go-to-market intelligence platform for cloud partners and SaaS companies. We built its security programme across five areas and kept our team on call around the clock, so a question from Wyra’s engineers or from the auditor never waited for the next working day.

Wyra had its SOC 2 Type 1 report and its ISO 27001 certification within two months of kickoff, and it has since come back to us for its Type 2.

  • Cloud security
  • Endpoint security
  • People
  • Infrastructure
  • Policies and procedures

“What you’ve delivered for Wyra has been truly exceptional — SOC 2 and ISO 27001 in such a short timeframe is no small feat. Couldn’t have asked for a better partner on this journey.”

Ravi, Founder, Wyra.AI
Read the full story
Personaify

AI for commercial real estate

Type 1SOC 2 report across all five Trust Services Criteria

How Personaify reached SOC 2 Type 1

Personaify builds AI that reviews leases, design drawings and project documents for commercial real estate teams, so landlords and tenants can open new spaces faster. Its customers hand over their own documents, so they want to see how that data is protected before they sign.

We ran the gap assessment against the Trust Services Criteria, reviewed the policies and brought them in line with the criteria, built the control matrix with Personaify’s engineers and reviewed the evidence control by control. The auditor then examined the controls and issued Personaify’s SOC 2 Type 1 report.

  • Gap assessment
  • Policy review
  • Control build
  • Evidence
  • Audit support
Read the full story
Forsys

Quote-to-cash consultancy

4 monthsfrom the start of the testing period to the SOC 2 Type 2 report

How Forsys reached SOC 2 Type 2 across all five criteria in four months

Based in Milpitas, California, Forsys implements revenue and quote-to-cash systems for large enterprises, and an enterprise deal was waiting on its report. The scope covered all five Trust Services Criteria, so every control had to be in place and operating before the testing period began.

We mapped Forsys’s own policies to the criteria, built the evidence programme with its security team and supported them through a Type 1 and then a Type 2 report. The auditor issued the Type 2 report four months after the testing period began.

  • Security
  • Availability
  • Processing integrity
  • Confidentiality
  • Privacy

“Our SOC 1 and SOC 2 journey couldn’t have been made more simple. TCSA guided us throughout and helped us unblock our enterprise deal.”

Murli, CISO, Forsys Inc.
Read the full story
The record

What nine years add up to.

1,000+audits since 2017
300+SOC 2 engagements
100+SOC 1 engagements
10,000+vulnerabilities found by our own testers
500+professionals trained
200+startups
20+frameworks
5markets: India, the US, the UK, Australia and the UAE

Audits count our audit engagements only. Penetration tests are counted on their own. How we count

How we work

We prepare. Independent auditors sign.

What we do

01

Scope

We start with what your customer or regulator is asking for, then agree the framework, the systems in scope and a fixed fee.

02

Gap assessment

We compare what you have with the framework, control by control, and give your engineers a plan they can work from.

03

Build

We write your policies, help your team put the controls in place and build the evidence your auditor will test.

04

Audit

We prepare your team, join the audit sessions and answer the auditor’s questions alongside you.

Who signs

SOC

SOC 1 and SOC 2 reports

Examined and signed by an independent CPA firm, licensed in the US and enrolled in AICPA peer review. Its name and licence are printed on your report.

ISO

ISO certificates

Issued by an independent certification body after its own audit. We prepare you for it and never certify the systems we helped build.

Tests

Penetration tests

Run by our own testers, with a report and a retest of your fixes.

Proof

In their words.

Quotes verbatim from G2. Company names added where the client confirmed them.

Verify on G2
They expertly mapped the overlapping controls between SOC 2 and ISO 27001, which saved us from duplicating work.
Jasreet Kaur B.Silicon Physical Design Engineer · Small-BusinessSOC 2 + ISO 27001 · August 2026
Instead of simply providing generic templates or checklists, their team took the time to understand our environment and requirements.
Anand .Market Risk Analyst · Mid-MarketCompliance readiness · September 2026
The team’s willingness to work with us and ease of communication.
sam v.CEO · Small-BusinessSOC 2 Type I + ISO 27001 · August 2026
They delivered the project with speed, accuracy, and cost-effectiveness.
Maneet P.Mid-MarketSOC 2 · August 2026
My only regret is that we didn’t engage them sooner in our compliance journey, which would have saved us even more time.
Mahesh Raju C. · XonarSmall-BusinessSOC 2 · GRC · August 2026
They were always responsive and willing to go the extra mile whenever we had questions or needed guidance.
Chandan J. · DsiderSmall-BusinessSOC 2 Type I · August 2026
Managing the auditor relationship on our behalf was especially valuable — it took a lot of pressure off our internal team.
Achyut B.Senior Software Engineer · Small-BusinessSOC 2 + ISO 27001 · September 2026
Their focus on ensuring that we were genuinely audit-ready rather than simply completing documentation.
Ravi V.Founder & CEO · Mid-MarketSOC 2 Type II · August 2026
The guidance was not generic or simply based on a standard checklist — they suggested practical approaches that made sense for our business.
Verified UserInternational Trade and Development · Small-BusinessSOC 2 + ISO 27001 · September 2026
What I like best is the hands-on support and clear guidance throughout the SOC 1 and SOC 2 process.
Sai Sudha S. · ExcersSmall-BusinessSOC 1 + SOC 2 · September 2026
Where to find us

Gurugram and Bengaluru.

Registered office

Gurugram

7th Floor, Worxspace, Welldone Tech Park,
Sohna Road, Sector 48, Gurugram, Haryana 122018

Office

Bengaluru

Mangalam Ecstasy, 8th Floor, Hosabasavanapura,
Bengaluru, Karnataka 560049

Tell us what you are working towards.

A customer’s security questionnaire, a first SOC 2, a DPDP deadline, an ISO 27001 renewal or a CERT-In audit. We deliver CERT-In audits, end to end, with our CERT-In empanelled partners. A short call is the quickest way to see what the work involves, how long it usually takes and what it will cost.

Get in touch.

Book a free consultation or send us your requirements. We respond within 24 hours.

Send us your requirement.

01Your details
02What is it about?
03Send